ISO 27001:2022 certified
Independently audited information-security management system.
Your credential data is protected by enterprise-grade security, independent certification, and privacy-by-design, so you can issue with confidence.
ISO 27001:2022 certified • GDPR compliant • Zero incidents in 3+ years
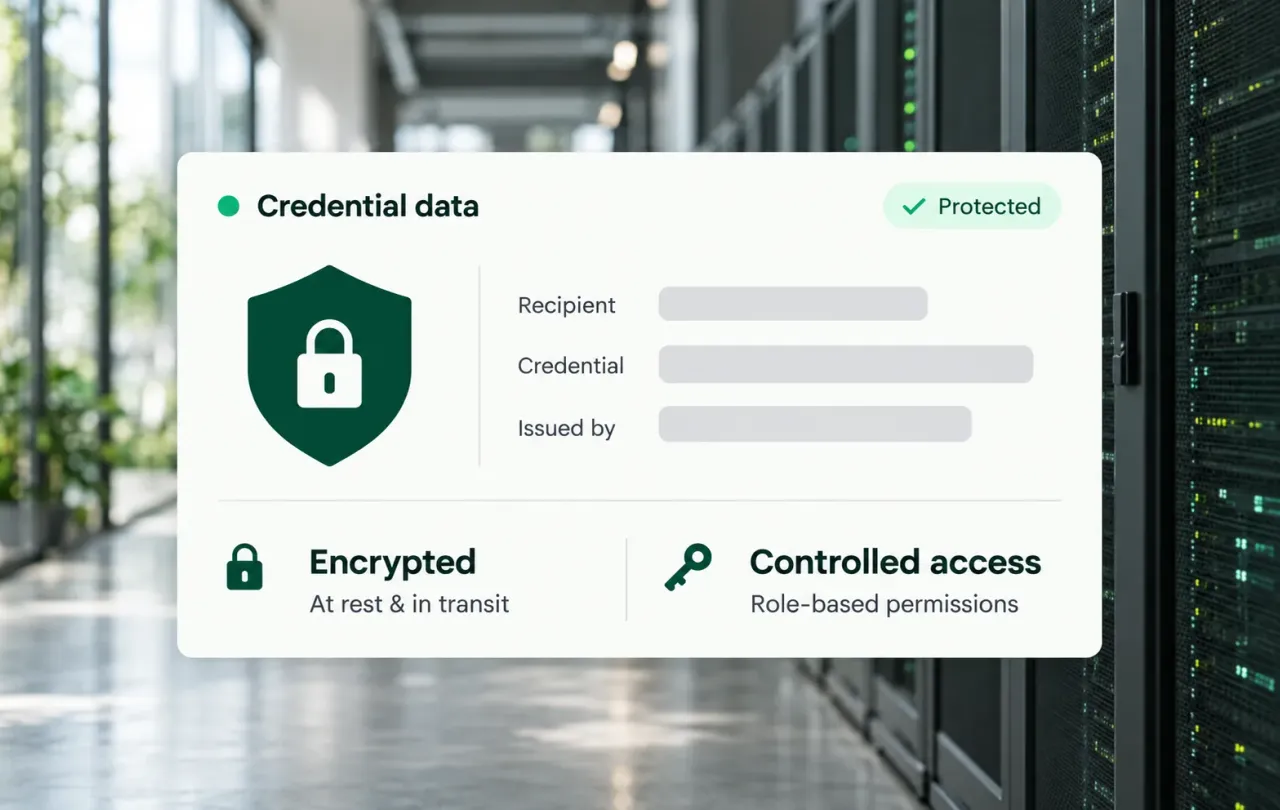
Sertifier is ISO 27001:2022 certified, GDPR compliant, and has maintained zero security incidents in over three years. Credential data is encrypted with AES-256 at rest and TLS 1.2+ in transit, hosted on Google Cloud Platform with configurable EU or US data residency.
Certifications & compliance
Sertifier meets the certification and privacy standards enterprise procurement and RFP teams expect, audited by third parties and backed by clear data-processing terms.
Independently audited information-security management system.
Privacy-by-design, with data subject rights fully supported.
Aligned with US state privacy law and children’s-privacy requirements.
A participant for compliant cross-border transfers, plus SCCs where applicable.
Sent on request; Sertifier acts as your Data Processor.
Data protection
AES-256 encryption at rest and TLS 1.2+ in transit for all credential data.
Role-based access control, SSO and SCIM for provisioning, and full audit logs.
You control what goes into each credential, typically just a name and email.
Infrastructure & reliability
Sertifier runs on Google Cloud Platform with a serverless architecture that auto-scales, plus business continuity and disaster recovery processes to keep credentials available.
Serverless architecture that auto-scales with your issuance volume.
EU (europe-west1) or US (us-east1 / us-central1), configurable per customer.
Business continuity and disaster recovery processes keep credentials available.
Testing & monitoring
Conducted annually by a third party, most recent test in January 2026.
Ongoing scanning via Google Cloud-native security tooling.
Infrastructure and systems monitored around the clock.
Privacy & your data
Sertifier acts as a Data Processor; your organization remains the Controller. We process the minimum needed to issue and verify credentials, typically a recipient’s name and email, the credential fields you choose, and admin business-contact details.
We use a limited set of vetted sub-processors; details are available under our DPA.
A standard Data Processing Agreement is available whenever you need one.
Choose EU or US storage to match your compliance requirements.
We support access, correction, and deletion requests for your recipients.
Documents & resources
FAQ